Can a company hold its IT service provider and an employee of the service provider liable when the employee uses privileged access to infiltrate the company’s computer systems and extract confidential commercial information?
In Gas Malaysia Energy and Services Sdn Bhd & Anor v Rishveer Singh Jaswant Singh & Anor [2026] CLJU 3384, the Kuala Lumpur High Court considered the civil liability of an IT service provider and its employee (“First Defendant”) following an unauthorised intrusion into the Plaintiffs’ computer systems, resulting in the exfiltration of approximately 621GB of corporate data.
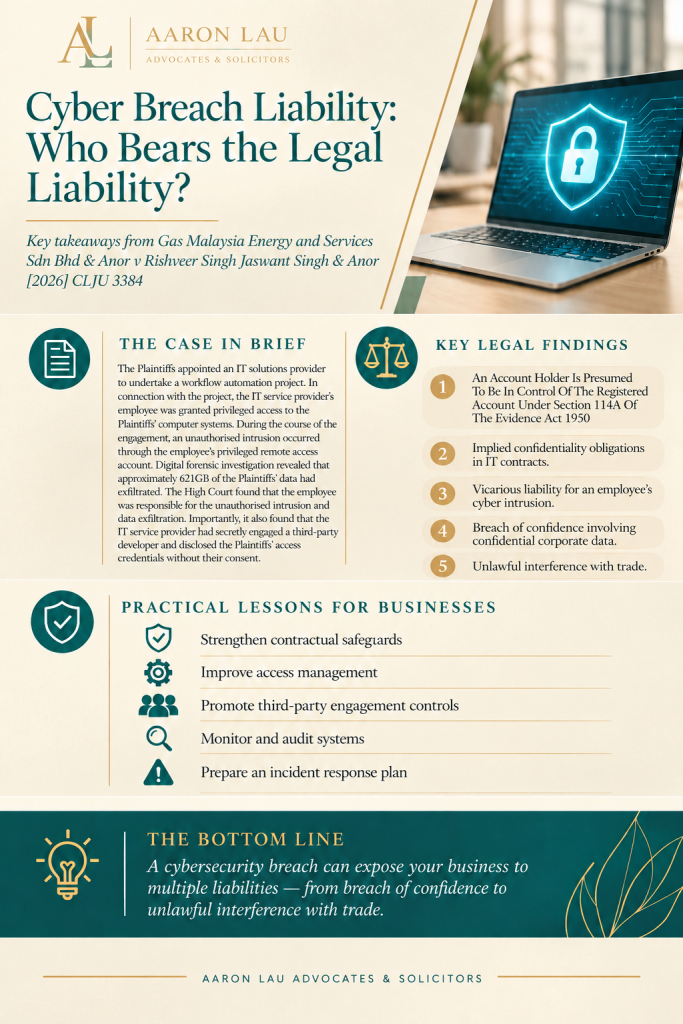
In this case, the Plaintiffs appointed an IT solutions provider to undertake a workflow automation project. In connection with the project, the First Defendant was granted privileged access to the Plaintiffs’ computer systems.
During the course of the engagement, an unauthorised intrusion occurred through the employee’s privileged remote access account. Digital forensic investigation revealed that approximately 621GB of the Plaintiffs’ data had been exfiltrated to a MEGA cloud storage account.
Section 114A of the Evidence Act 1950: Can a Person Be Held Responsible for Online Activities Under Their Account?
One of the important aspects of this decision was the Court’s application of section 114A of the Evidence Act 1950, which provides for a statutory presumption of identity in relation to online publications.
In simple terms, the provision allows a court to presume that a person is responsible for an online publication in certain circumstances, including where:
-
Their name, photograph or pseudonym appears on the publication identifying them as its owner, host, administrator or editor;
-
They are registered as the subscriber of the network service through which the publication originated; or
-
They have custody or control of the computer from which the publication originated.
However, this presumption is rebuttable. This means that the person concerned may present evidence to prove that they were not responsible for the publication.
In this case, the unauthorised intrusion was carried out through a privileged remote access account registered to the First Defendant, known as “wms_rishveer”. The Court held that section 114A of the Evidence Act 1950 was engaged and that the legal burden shifted to the First Defendant to prove otherwise.
The First Defendant denied involvement and suggested that an unknown person could have used his account. However, the Court found that a mere denial or the suggestion that other people could potentially have accessed the account was insufficient to rebut the statutory presumption.
Ultimately, the Court found that the First Defendant had failed to rebut the presumption under section 114A of the Evidence Act 1950. Importantly, the Court went further and independently found, on a balance of probabilities, that he was responsible for the intrusion and the extraction of the Plaintiffs’ data.
An IT Service Provider May Be Liable For Fundamental Breach Of Contract
In this case, the Letter of Award issued by the Plaintiffs did not contain an express confidentiality clause governing access credentials. However, after considering the principles in the landmark decision of the Privy Council in BP Refinery (Westernport) Pty Ltd v. Shire of Hastings, where five conditions must be satisfied before a term can be implied into a contract, the Court held that an implied term existed requiring the IT service provider to keep the Plaintiffs’ system credentials confidential and refrain from disclosing them to third parties without consent.
The Court further held that the IT service provider’s undisclosed engagement of a third-party developer, coupled with the disclosure of privileged access credentials, constituted a fundamental breach going to the root of the Letter of Award. Consequently, the Court allowed the Plaintiffs to rescind the Letter of Award.
This decision highlights the importance of clearly defining confidentiality obligations, access restrictions and third-party engagement in commercial IT contracts. Although the Plaintiffs in this case successfully satisfied the requirements in BP Refinery for implication of contractual terms, it would be ill-advised for businesses to take such “protection” for granted as implication of contractual terms is not automatic, and the outcome is dependent on the facts and circumstances of each case.
An Employer May Be Vicariously Liable For Its Employee’s Cyber Criminality
Here, the Court applied the principles of close connection and enterprise risk tests in GMP Kaisar Security (M) Sdn Bhd v. Mohamad Amirul Amin Mohamed Amir and held that the First Defendant’s wrongful conduct was closely connected to his appointment. In particular, the First Defendant was assigned as the principal point of contact for the project and was granted privileged access to the Plaintiffs’ systems through his employment with the IT service provider.The Court held that the IT service provider’s enterprise had materially created and enhanced the risk of the wrongdoing. Accordingly, the IT service provider was held vicariously liable for the employee’s (First Defendant) tortious acts. Importantly, an employer cannot necessarily avoid civil liability merely because the wrongful conduct was unauthorised or intentional.
The Defendants Were Liable For Breach Of Confidence
Applying the three-part test in Coco v A.N. Clark (Engineers) Ltd, the Court was satisfied that the Plaintiffs’ internal operational information and access credentials possessed the necessary quality of confidence. They were accessed by the defendants in circumstances importing an obligation of confidence. The information and access credentials had been subjected to unauthorised use or disclosures by the defendants. Consequently, the Court found both defendants liable for breach of confidence.Interestingly, the Court dismissed the Plaintiffs’ claim in conversion.
Following OBG Ltd v Allan and Malayan Banking Bhd v Charanjeet Kaur Sukhbir Singh, the Court held that conversion, under the existing position of Malaysian law, applies to tangible property rather than intangible digital information. Further, the plaintiffs had not been deprived of possession of their data, as the data had been copied rather than physically taken.
Nevertheless, the Court observed that the existing limitation of conversion to tangible property may warrant reconsideration in an economy where digital assets are increasingly valuable.
The Defendants Were Also Liable For Unlawful Interference With Trade
The Court further found both Defendants liable for unlawful interference with trade. It held that the unauthorised intrusion into the Plaintiffs’ computer systems and the exfiltration of their corporate data constituted unlawful means. The deliberate and covert nature of the acts, which were directed at the Plaintiffs’ own infrastructure, established the requisite intention to injure. Further, interference with the Plaintiffs’ trade was found to be the natural and probable consequence of compromising the operational data and access credentials of a gas utility company.What Should Companies Take Away From This Decision?
This decision serves as a reminder that cybersecurity risks do not necessarily originate from external hackers. They may also arise from employees, contractors or third-party service providers who have been granted legitimate access to a company’s computer system.
Therefore, companies should consider implementing the following precautionary safeguards to mitigate risks of unauthorised access leading to disclosure, misuse or exfiltration of confidential corporate information and trade secrets, particularly where such access is entrusted to third parties:- Contractual safeguards: Ensure IT-related service agreements contain express confidentiality, non-disclosure, data protection and cybersecurity obligations.
- Access management: Restrict privileged access credentials to authorised personnel and implement appropriate access controls.
- Third-party engagement: Require prior approval or mandate before contractors or IT service providers delegate work or grant access to subcontractors or external developers.
- Monitoring and auditing: Practise maintaining appropriate system logs and monitor privileged access to identify suspicious activities.
- Incident response: Establish a response playbook and internal procedure aimed at preserving digital evidence once suspicious activities have been identified. It is crucial to respond promptly and appropriately to prevent the loss, alteration or destruction of potentially relevant evidence. Affected devices and systems should be properly secured, access logs and relevant digital records ought to be preserved, and forensic imaging is carried out by qualified personnel. This helps maintain the integrity and admissibility of digital evidence should legal proceedings subsequently arise.
Ultimately, granting an IT service provider access to your company’s computer systems does not mean relinquishing control over your confidential information or compromising your company’s security obligations.
The decision demonstrates that an IT service provider may face substantial civil liability where its contractual obligations and the conduct of its employees result in the compromise of a client’s computer systems and confidential information.
Disclaimer: This article serves as general information purposes only, and does not constitute as professional or legal advice. Legal advice should always be sought before taking any action or refraining from taking any action based on its own facts.
If you require legal advice or wish to enquire about a matter discussed in this article, please contact us for further assistance.
How the first enquiry works
The enquiry process helps you understand what to prepare and how we can assess the next legal steps.
1. Confidential enquiry
Share the nature of your matter through the contact form or your preferred enquiry channel. Alternatively, click here to make an enquiry.
2. Initial review
We consider the issue, its urgency, the available information, and the key documents involved.
3. Legal direction
You receive practical guidance on possible next steps and what may need to be prepared.
4. Representation
Where representation is required, the matter is handled with preparation, care, and discretion.